Contract intake with provenance
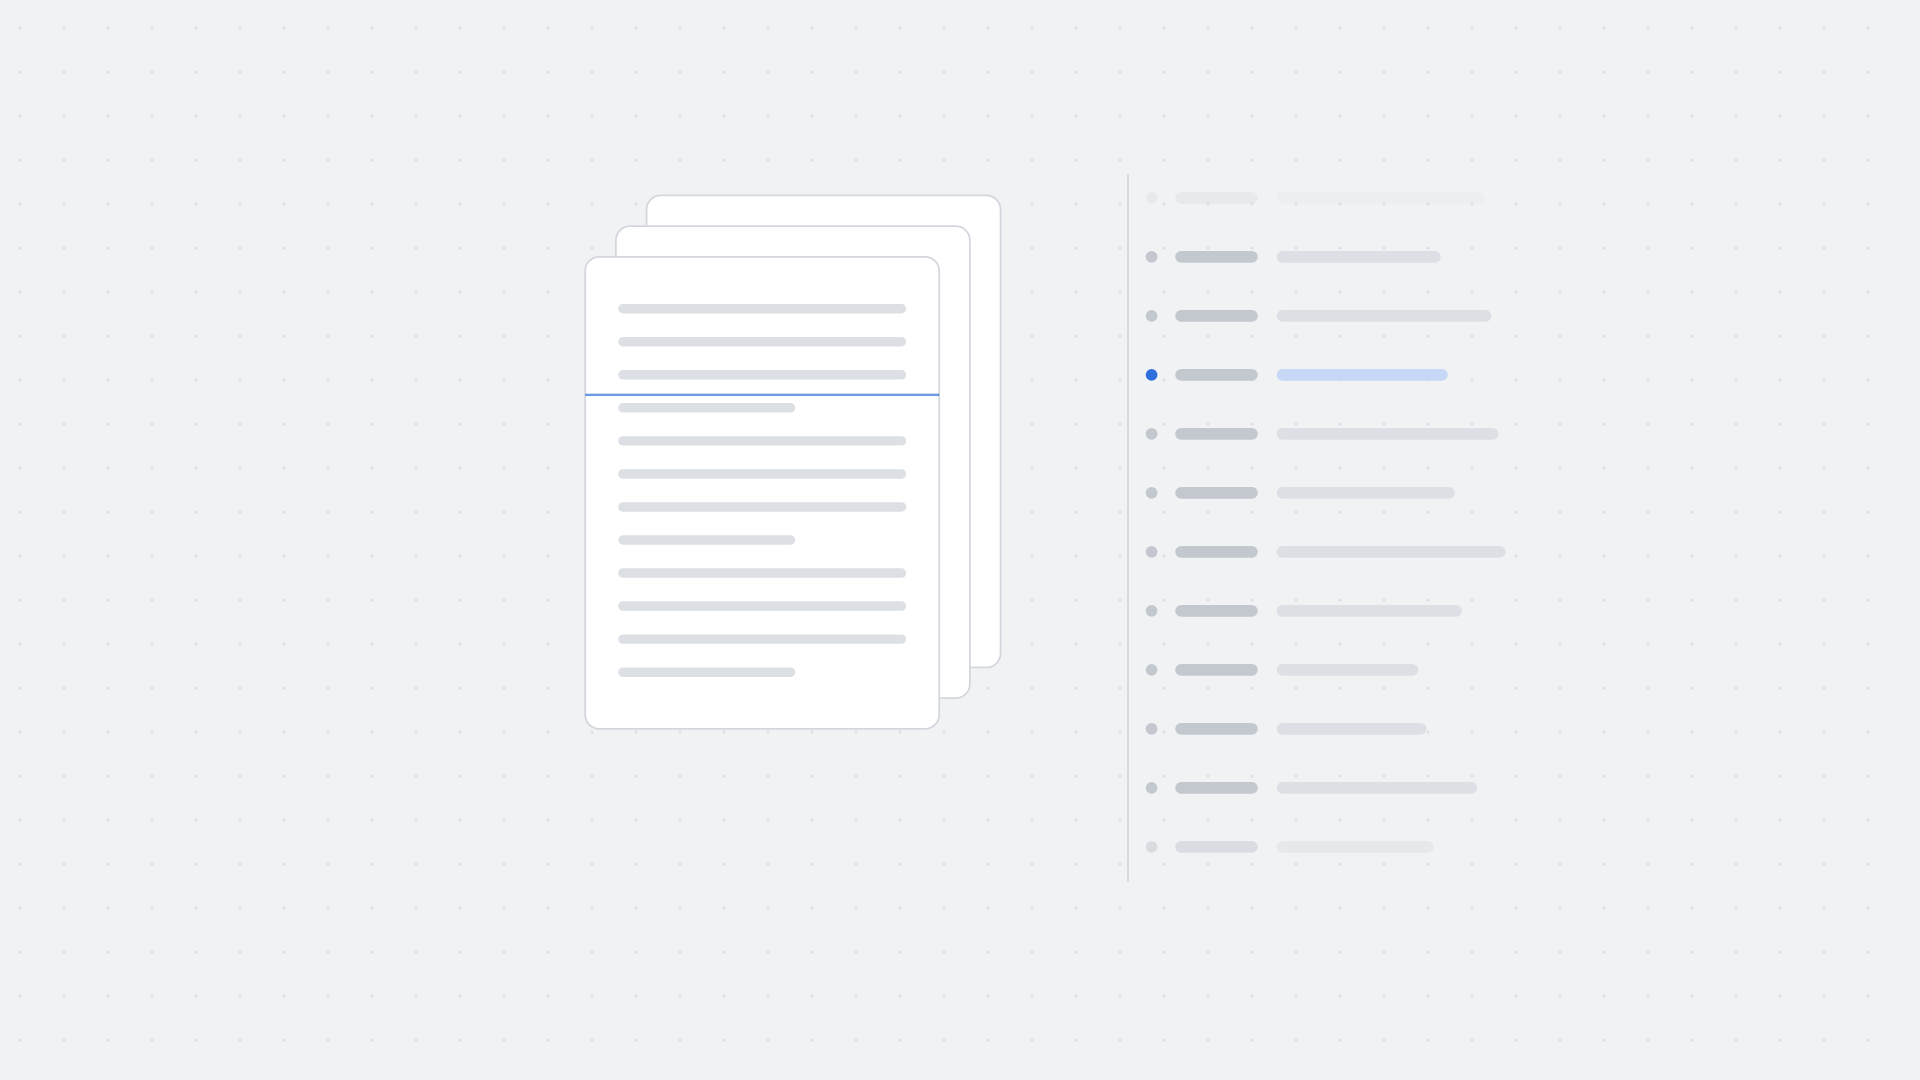
Arrangement data and clauses are extracted from the contract, each value linked to the passage it came from and scored for confidence. Low-confidence values are flagged for a person to review.
AI does the reading. Rules do the checking. People make the decisions, and the record shows all three.
Third-party risk teams spend their time reading contracts and questionnaires, chasing deadlines and assembling evidence when an inspection is announced. AI can take on the reading, but only if every output traces back to its source and every decision to a person.
AI where reading is the work, rules where the regulation is precise, and a named person behind every decision.
Arrangement data and clauses are extracted from the contract, each value linked to the passage it came from and scored for confidence. Low-confidence values are flagged for a person to review.
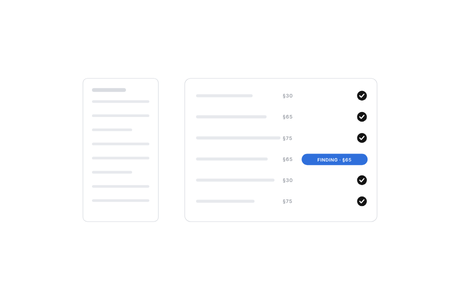
Clauses are checked against ΠΕΕ 178 §65 and EBA GL §75. A gap raises a finding citing the exact requirement; Legal confirms the verdict.
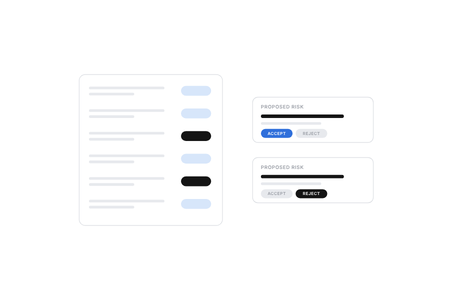
Completed due-diligence questionnaires are summarised, with inconsistencies and missing evidence flagged. Risks drawn from documents, answers and dependency data are proposed with their evidence for a named person to accept or reject.
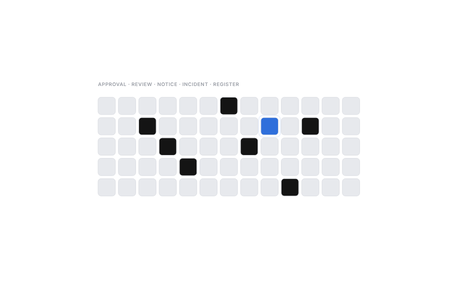
Regulatory deadlines, approval sequence, overdue reviews and missing notifications are checked continuously against the applicable rule pack, with named owners and escalation.
For any arrangement, a dated and attributed trail mapped to the regulatory requirement each step satisfies, ready for an ECB or Bank of Greece inspection.
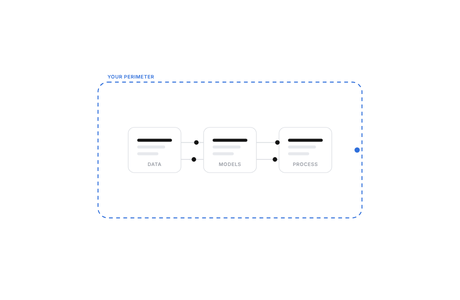
Deployed inside your perimeter, with AI on models your institution approves, and deployable so that no data leaves your environment. No AI output becomes a record until a person confirms it.
Talk to us about your institution's obligations.